Platform
Control every change, across every facility.
Govern requests and approvals, prove every decision, and hand off approved changes through controlled channels.
Govern
Govern every change
Multi-facility charge governance
Corporate charge standards with facility-level instances across your hierarchy of corporate, regions and sites. Effective-dated versions keep prior corporate and facility history.
Role-based requests and approvals
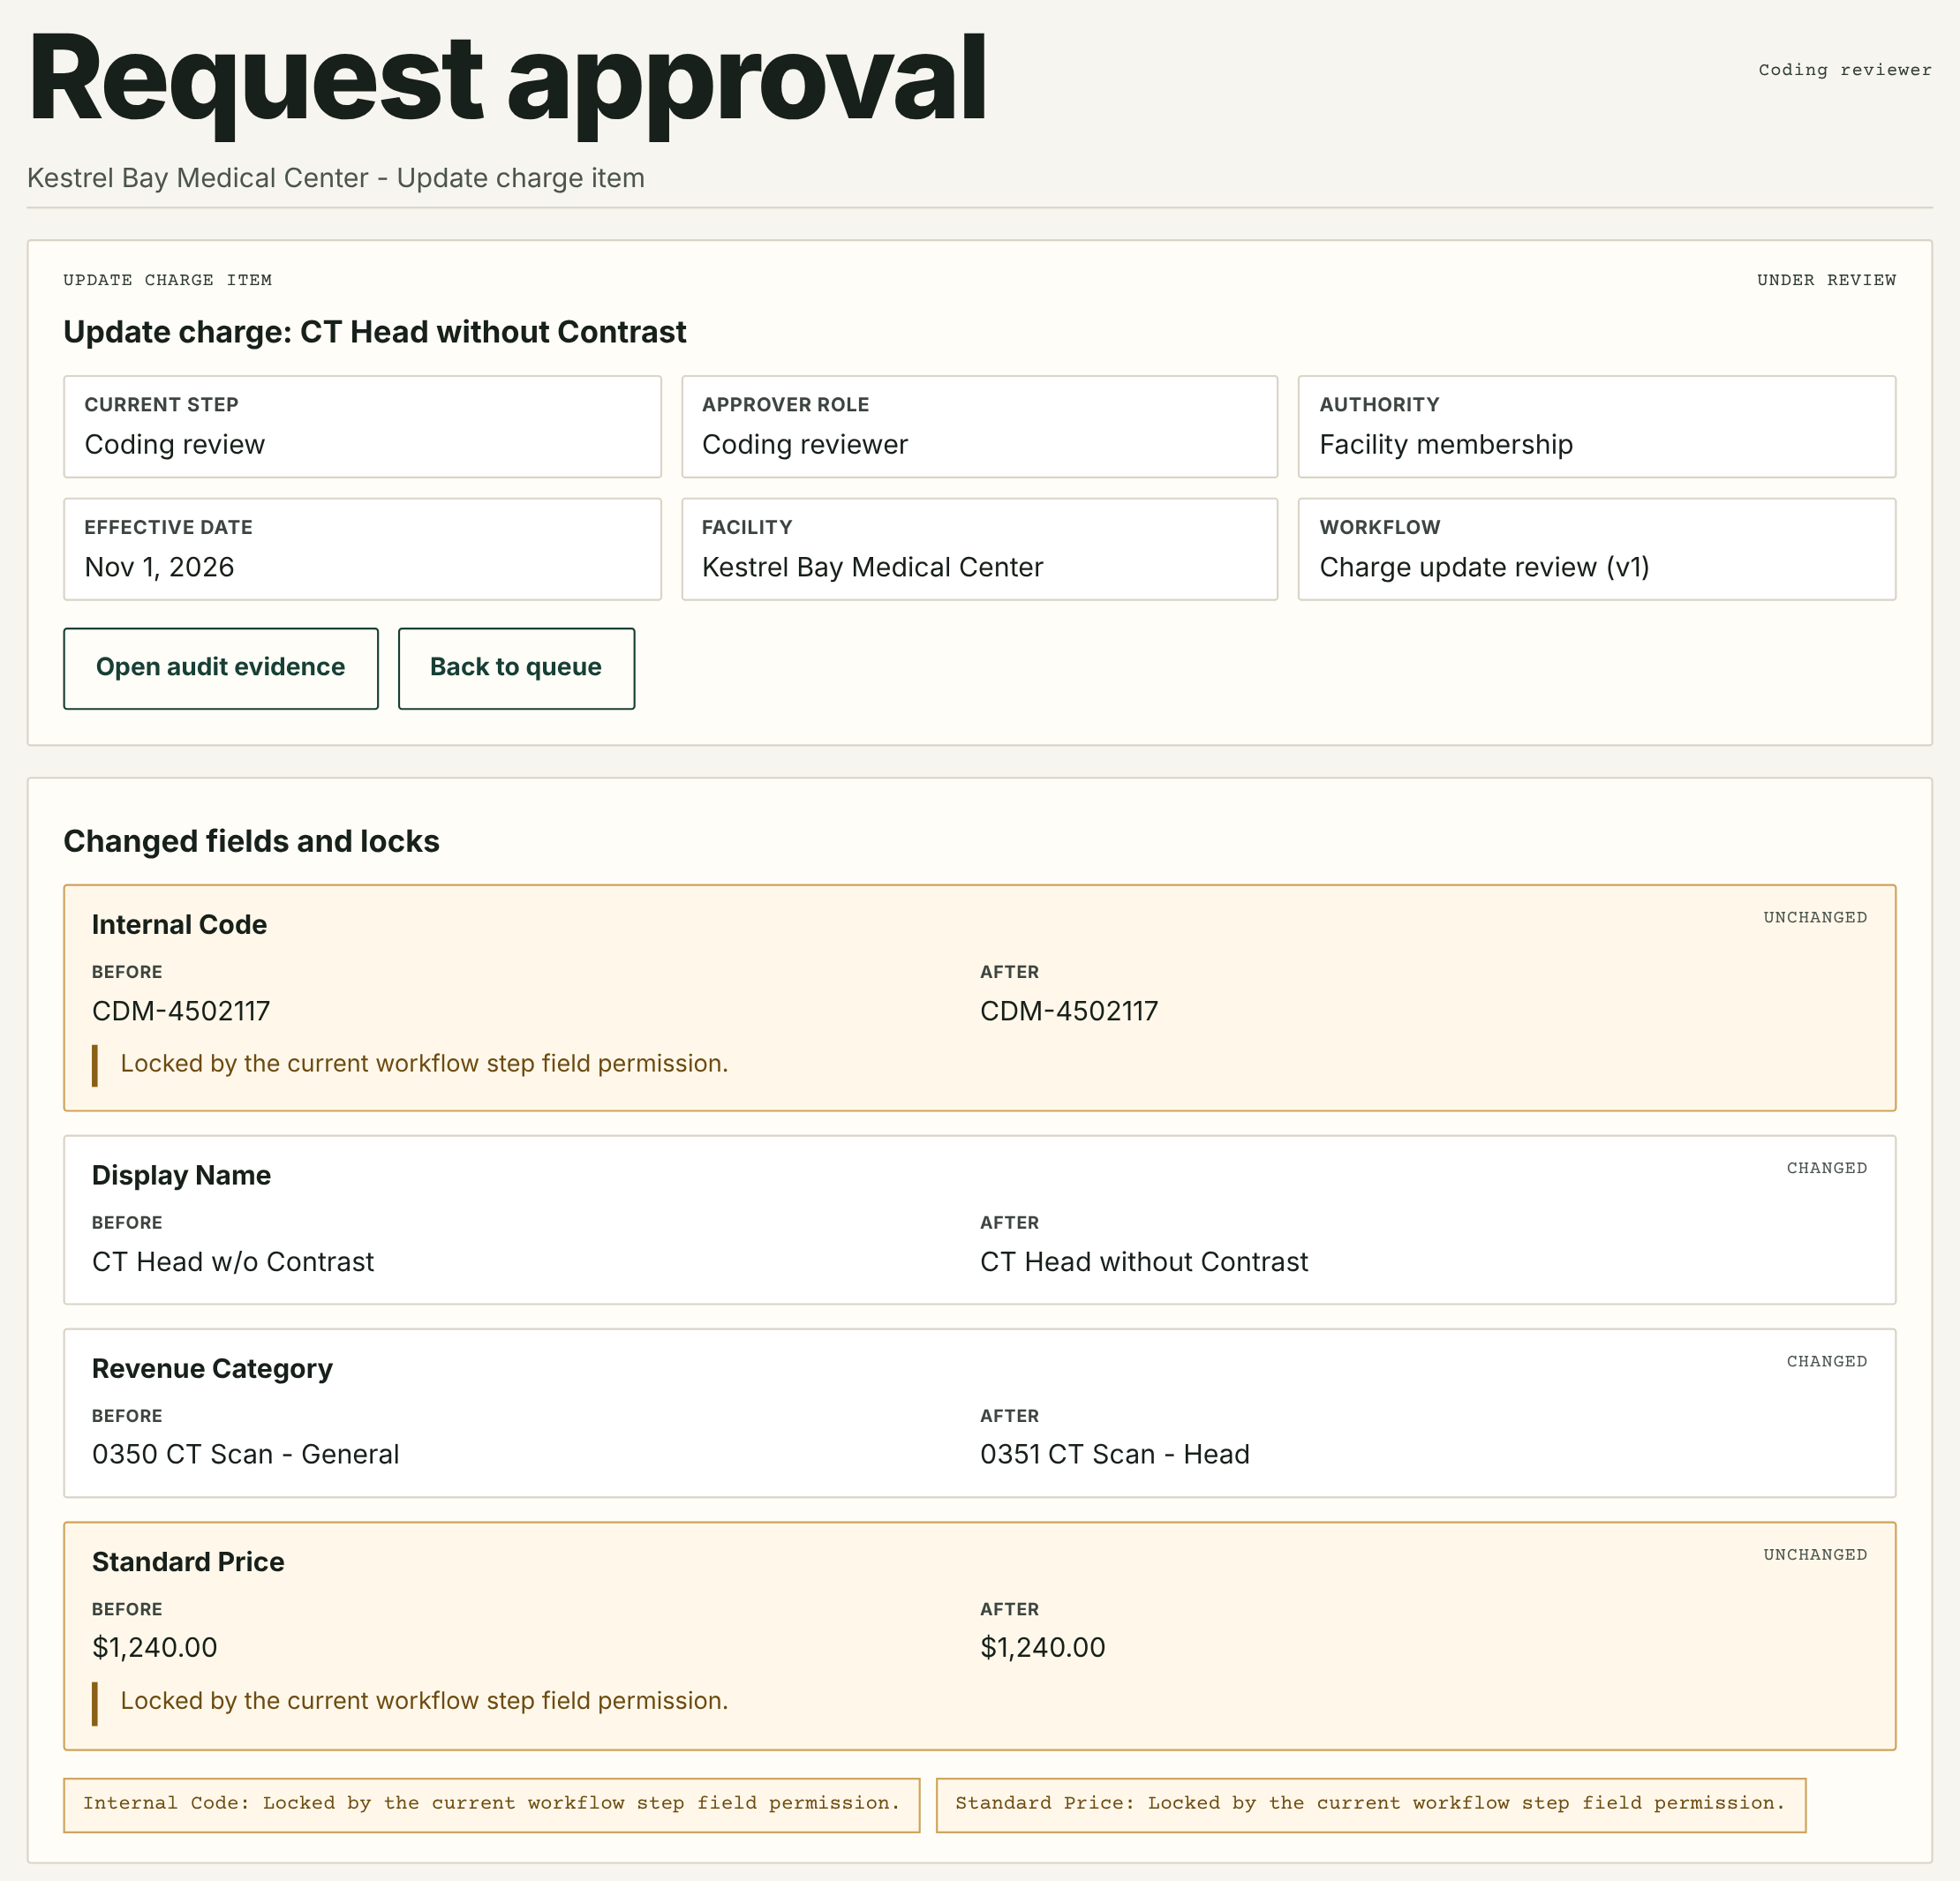
Requesters add, update or inactivate charges. Requests move through ordered steps, such as coding review and then finance. Reviewers approve, return or deny with a recorded reason. Nothing reaches the chargemaster until final approval.
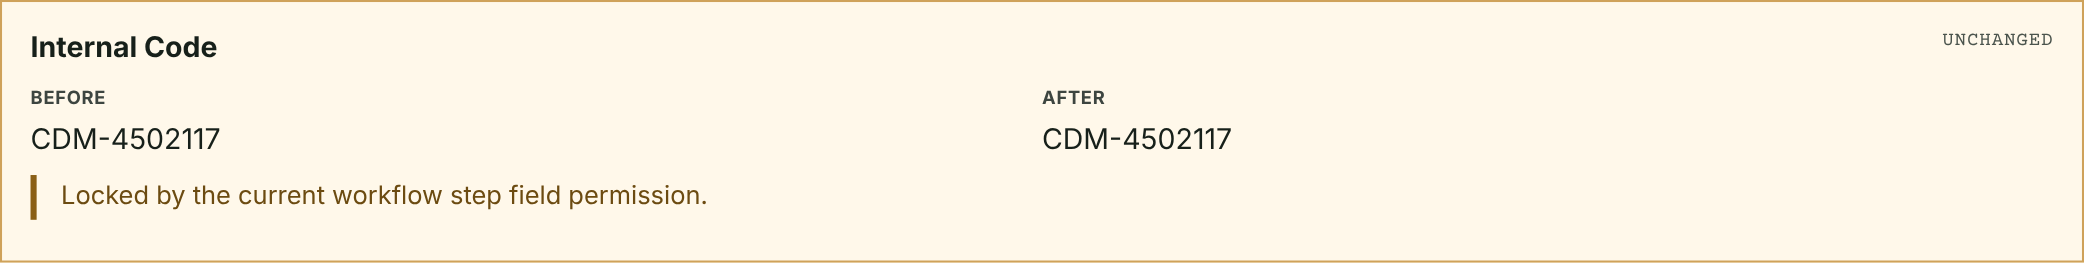
Field-level controls that can't be bypassed
Each step controls which fields a reviewer can change, by role and facility. Locked fields are shown in the screen and enforced on the server, so the rule holds even outside the screen.
Propagation with preserved overrides
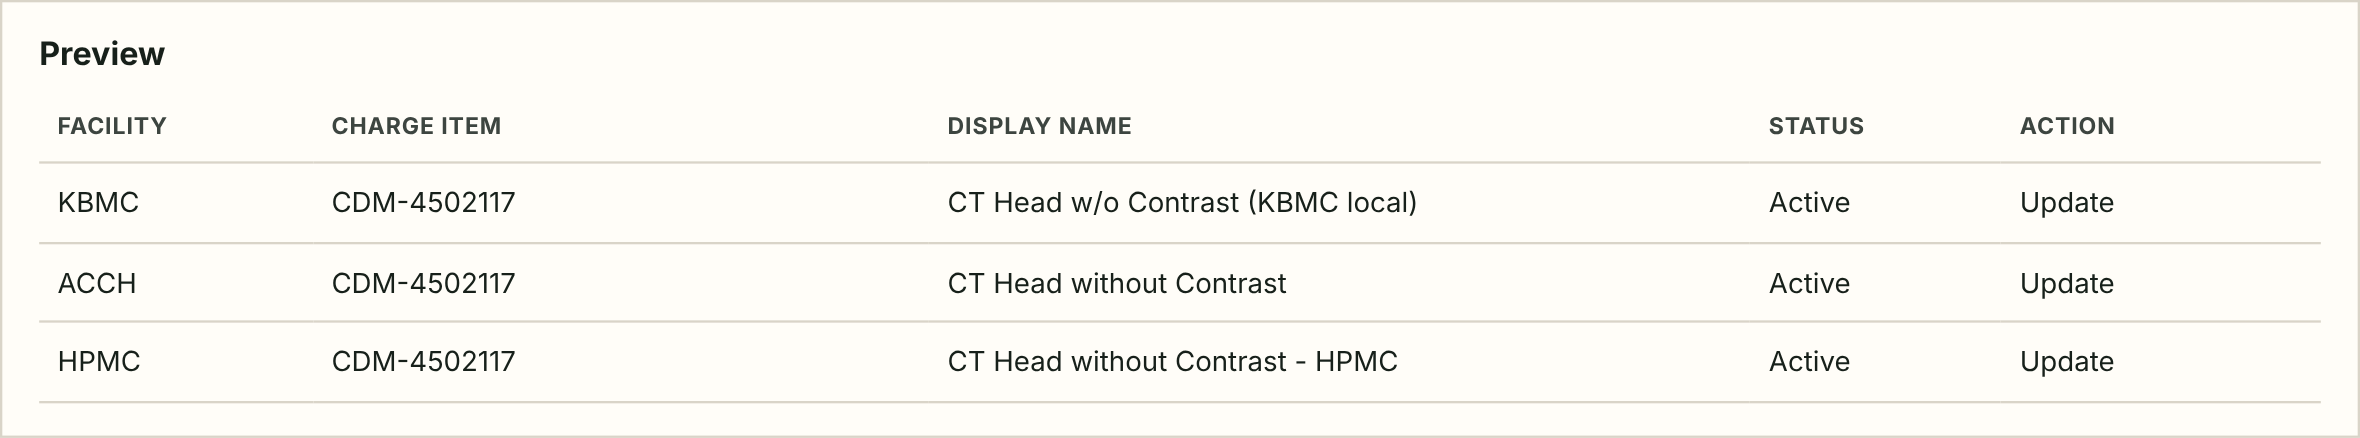
Corporate changes go out to the facilities you select while applicable local overrides are preserved. A charge can be inactivated at one site without touching the corporate item or other sites.
Configurable, versioned workflows
Administrators define steps and per-step field rules in a form-based designer, so finance can sit at whichever step your policy requires. Active versions can't be edited, and each request stays on the version it started on.
Approve from anywhere, with delegation
Reviewers decide from a mobile-optimized queue with field diffs and lock explanations. Time-bound delegation shows who is acting for whom.
Prove and connect
Evidence you can verify, handoffs you control.
Tamper-evident audit chain
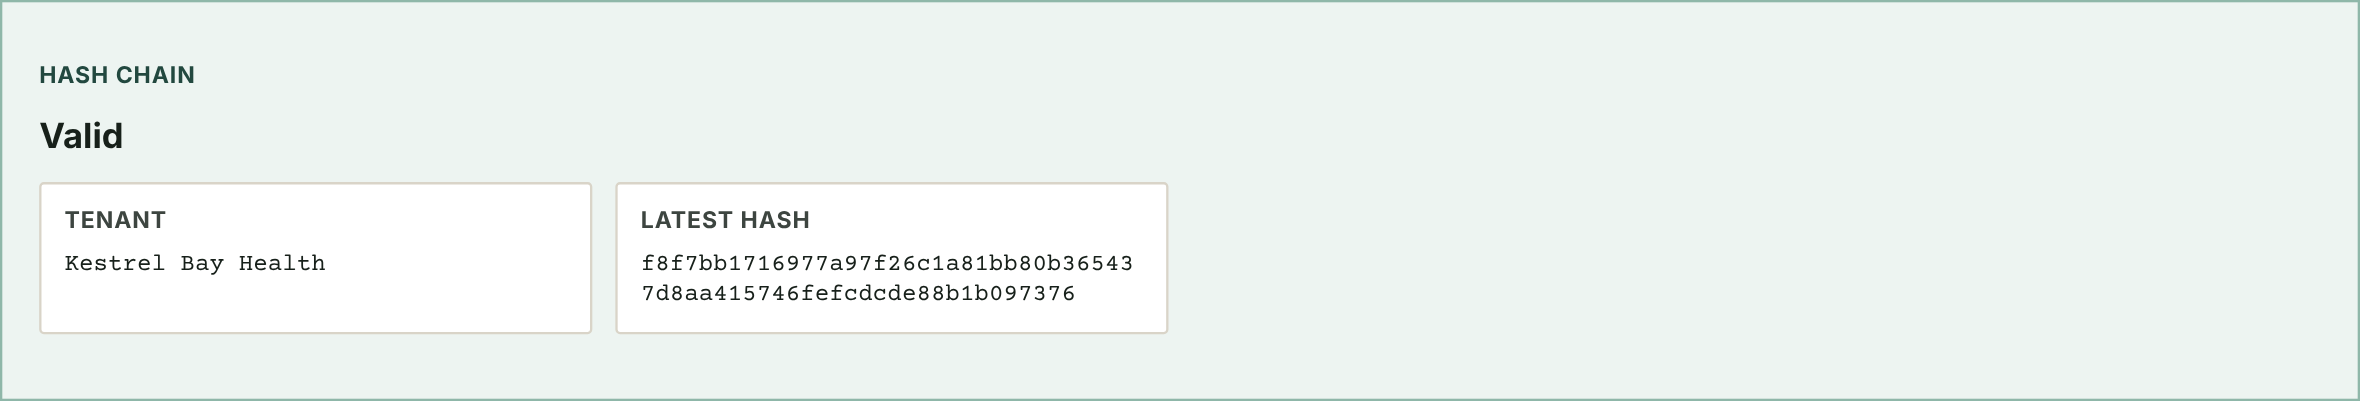
Every governed event is appended to a per-tenant SHA-256 hash chain. Audit records can't be updated or deleted, and verification shows the chain as “Valid”, so history is verified rather than taken on trust.
Evidence exports for auditors
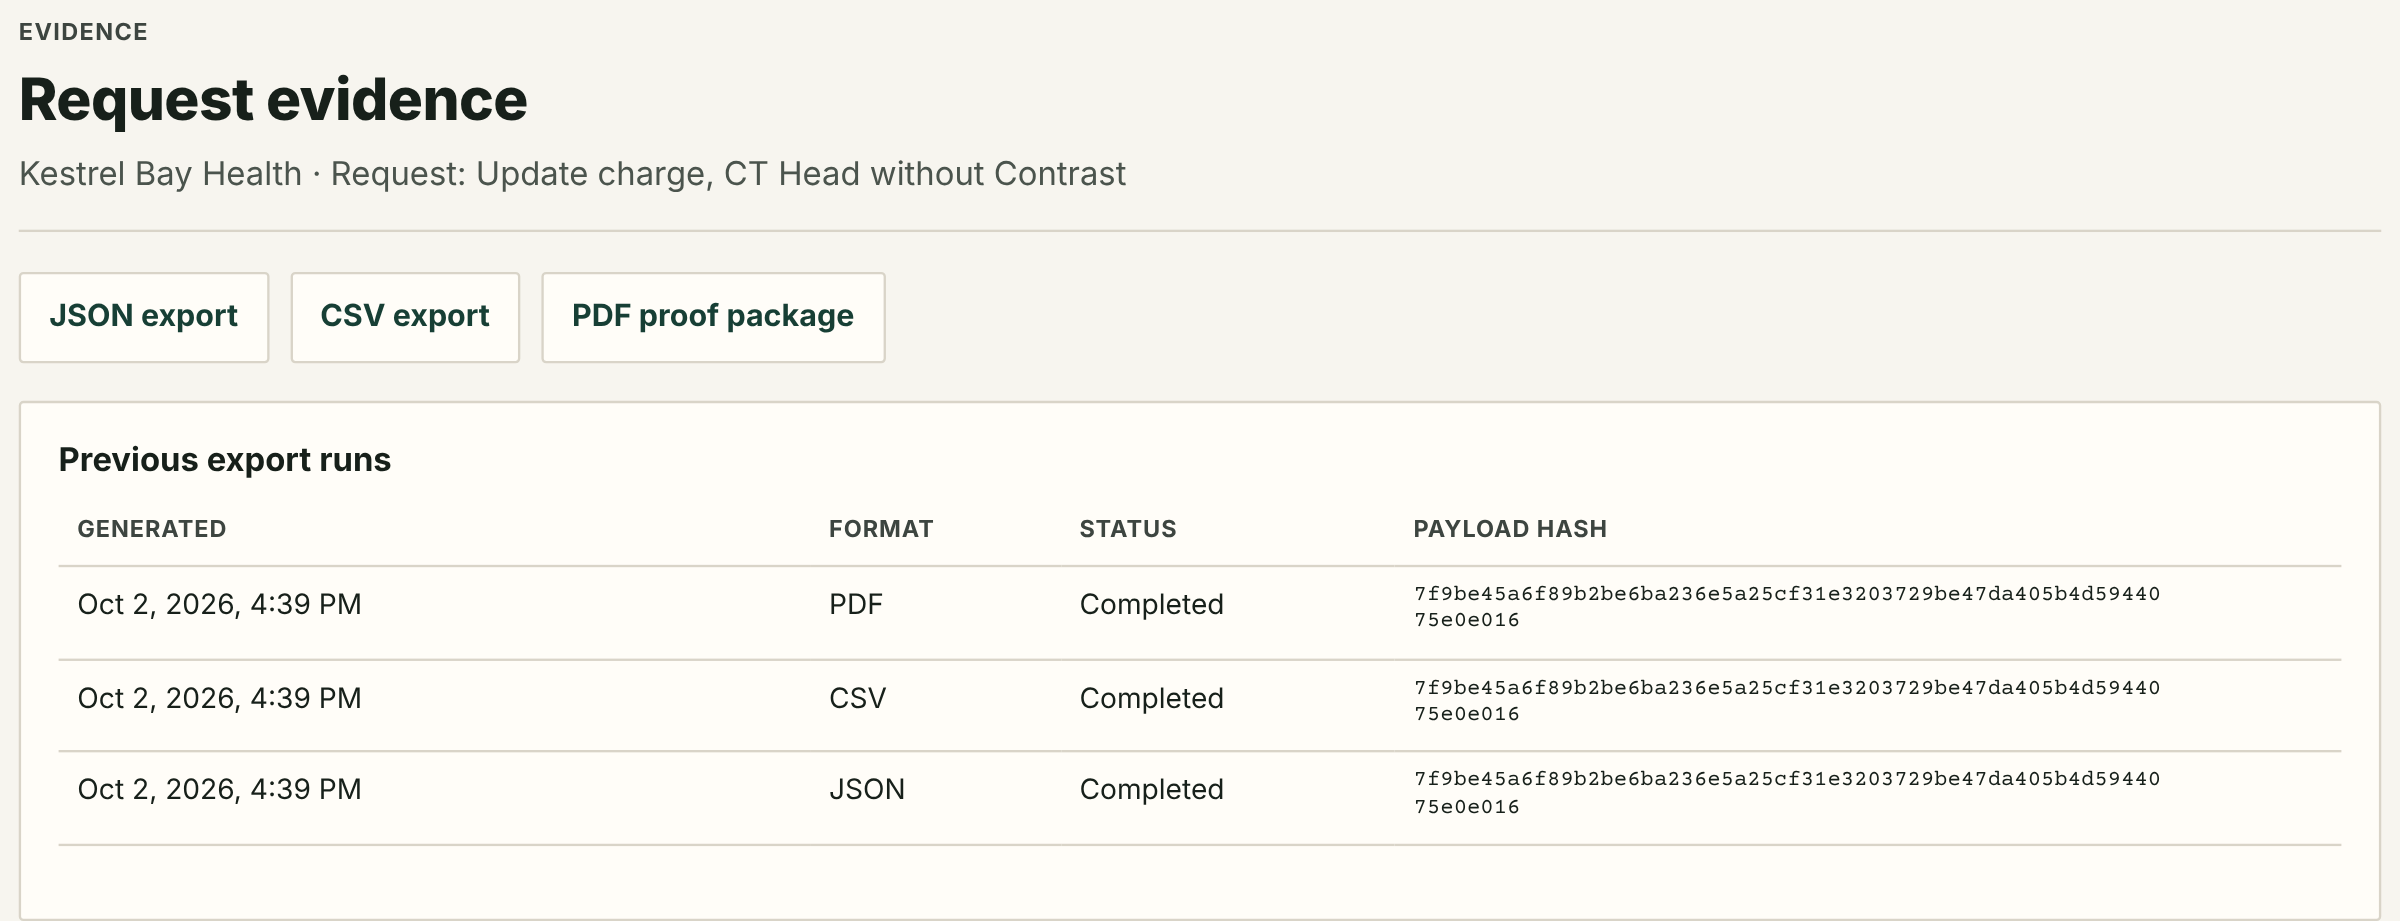
Auditors download a request's proof as JSON, CSV or a PDF proof package, with hash-verifiable manifests and tracked, repeatable export runs.
Governed downstream delivery
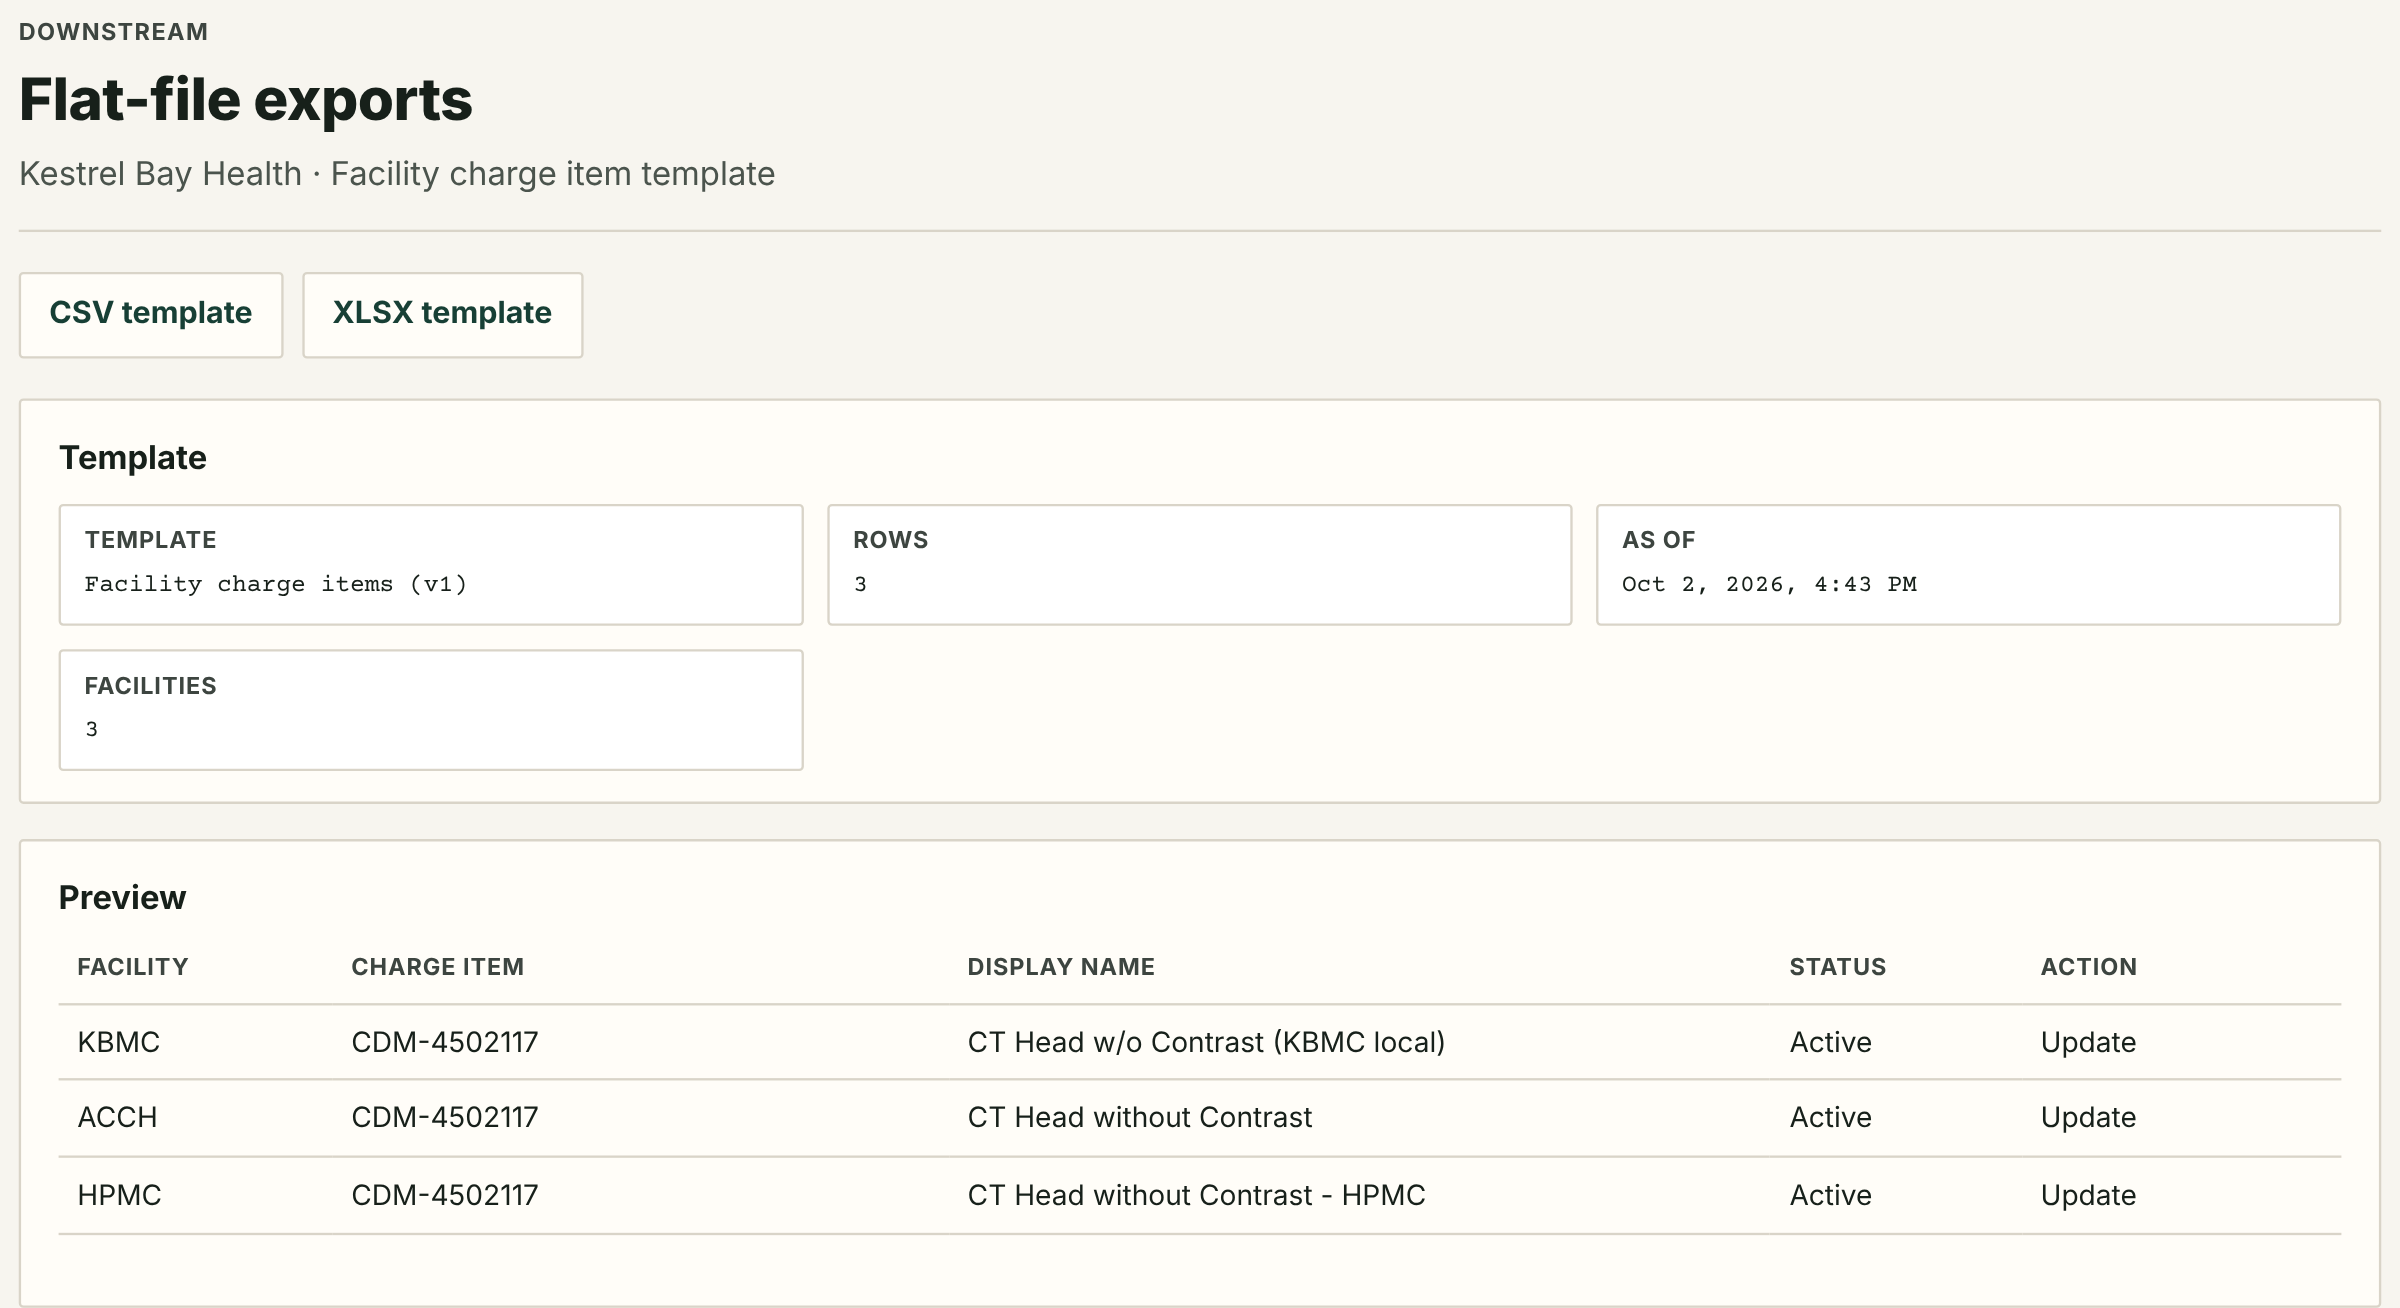
Two governed paths: scoped CSV and XLSX exports for any downstream system, and EHR connectivity over FHIR and HL7, delivered through Vellum's integration layer as part of your rollout. Both are limited to authorized facilities and recorded in the audit trail.
One integration layer for every system
Vellum's integration layer gives your health system access to all the EHR and system integrations it needs. Endpoint credentials are never stored in Vellum, and every outbound change is recorded with the approval that produced it.
Tenant isolation and access control
Database row-level security on every tenant-owned table keeps each tenant's data separate. Every governed change checks who is acting and records it. Admin pages are role-guarded, and users can't raise their own permissions.
Operational dashboard and administration
See requests in flight, queues, stale requests, cycle times and propagation and export activity. Administrators manage users and access, roles, facilities and workflows.
The complete Vellum platform
Delivered and configured as part of your Vellum rollout. Your rollout extends the core platform with enterprise identity, connected downstream systems through Vellum's integration layer, deeper administration and intelligent review, configured for your systems, facilities and policies.
Enterprise single sign-on
Your teams sign in through your organization's identity provider, with roles and facility scope mapped to Vellum permissions.
EHR connectivity over FHIR and HL7
Connectors to your EHR and billing systems are configured during your rollout and delivered through Vellum's integration layer, with delivery and acknowledgment tracking. Ask us about your systems.
Reconciliation and drift detection
Vellum compares connected systems with the governed record, flags mismatches and drift, and routes each exception to resolution.
Full chargemaster search and bulk import
Bring your existing chargemaster in through validated bulk import, then search and browse it across facilities.
Propagation and override administration
Operators launch, preview and approve corporate-to-facility propagation, and manage facility overrides and their effective dates.
Delegation, notifications and escalation
Administrators set up and revoke delegations. Reviewers are notified when a decision is waiting, and overdue requests escalate.
Signed manifests and external audit anchoring
Evidence packages carry signed export manifests, and checkpoints of the audit chain are anchored outside Vellum, so verification doesn't depend on Vellum alone.
Rules-based checks and AI-assisted prioritization
Validation rules catch likely errors before approval, and AI-assisted suggestions help reviewers prioritize. People make every decision.
CMS machine-readable files
Supports preparing CMS machine-readable files from governed charge data, so published files reflect approved changes.
Item master and formulary
Extend the same request, approval and evidence model to item master and formulary data.
One governance model, every domain. Each capability uses the same governed request, role-based approval, field-level control and tamper-evident evidence trail as the core platform.
Information current as of October 2026. The capabilities in this section are delivered and configured as part of your Vellum rollout, with scope set out in your SOW.
Talk to us
Book a working session on your chargemaster workflow. We'll walk through request, approval and evidence for your facilities with your finance, revenue integrity, chargemaster, compliance and IT teams.
Email [email protected]